The number of network-connected devices across IoT, robotics, commercial drones, autonomous vehicles, and smart factories continues to surge. In a world driven by Physical AI, establishing Device Trust--verifying whether a communicating hardware node is authentic--becomes a critical security imperative.
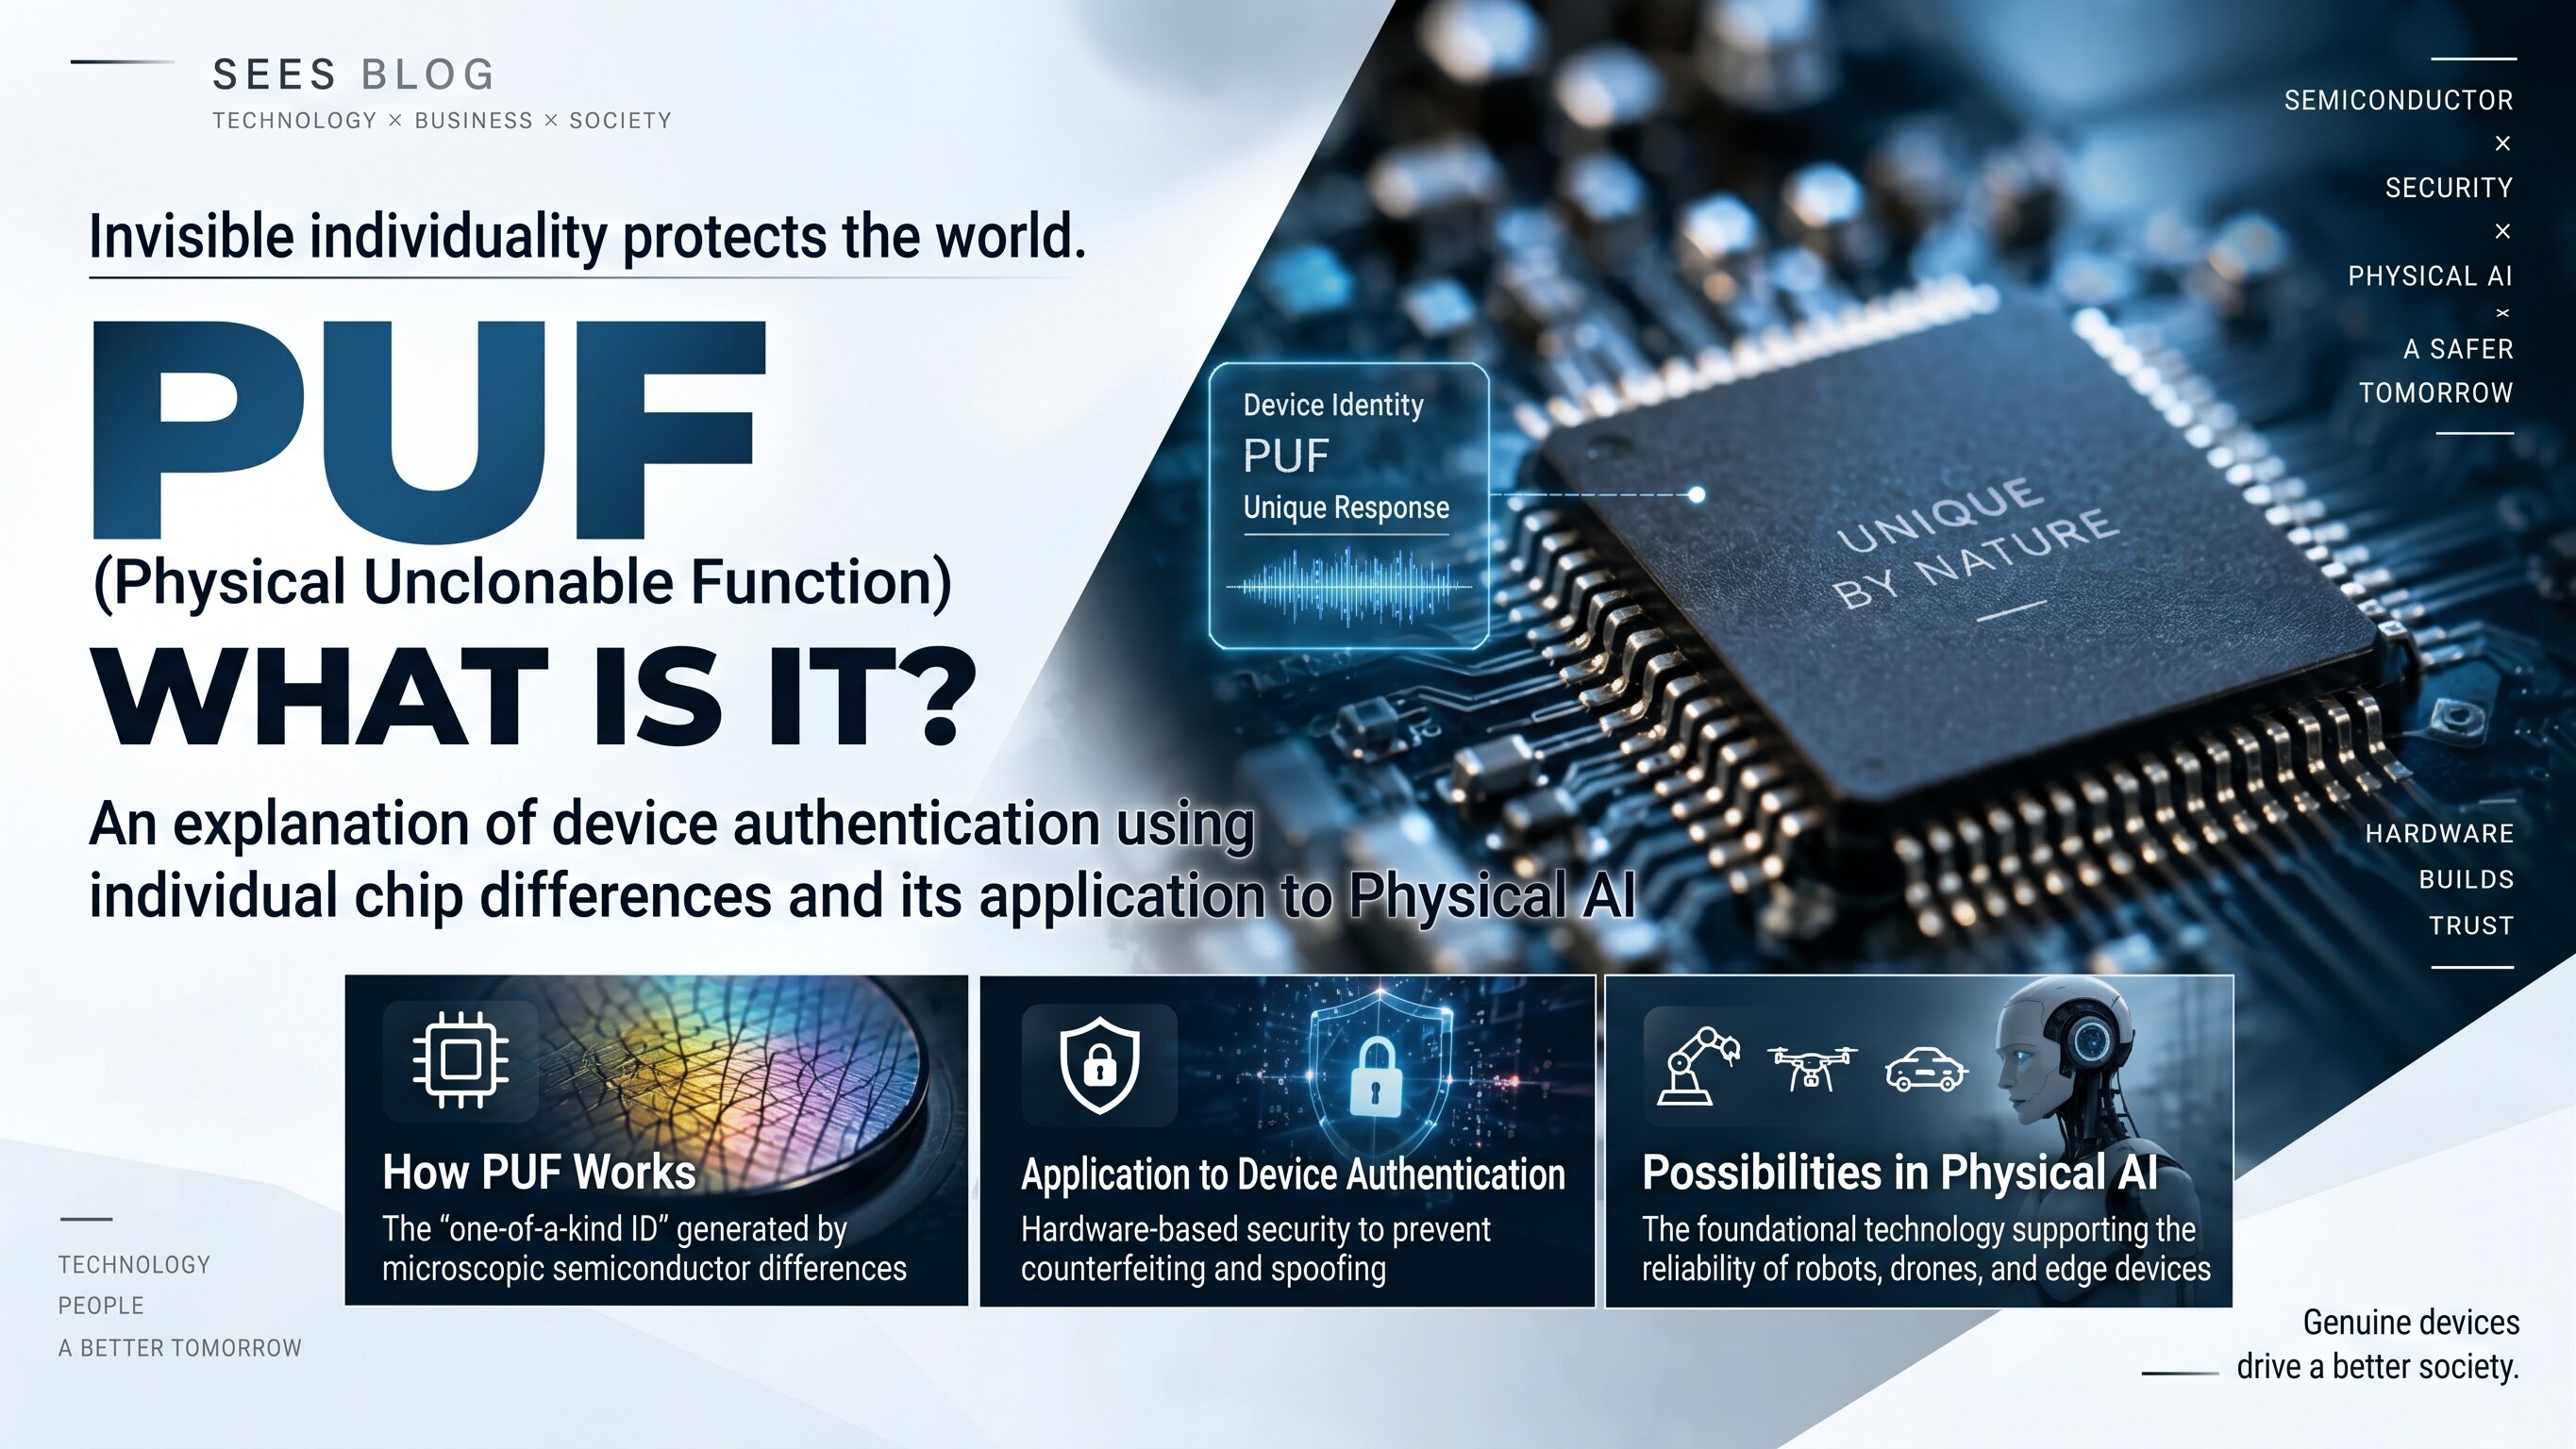
A PUF (Physical Unclonable Function) is a hardware security technology that generates unique response signatures by leveraging microscopic, unavoidable physical variations introduced during semiconductor manufacturing. Acting as a "semiconductor fingerprint," PUF is being deployed for hardware authentication, cryptographic key generation/derivation, and Machine Identity management.
- How PUFs (Physical Unclonable Functions) work at a fundamental level
- Why microscopic variations occur even among identically manufactured chips
- Key differences between PUFs and standard digital device IDs
- How PUFs differ from TPMs and Secure Elements
- Why Device Trust is paramount for Physical AI architectures
- Combining PUFs with Hash Chains for end-to-end security
- The difference between generic PUF implementations and SEES Chip Fingerprints
- The Physical AI Trust Infrastructure envisioned by SEES
- What Is a PUF?
- Why Microscopic Physical Variations Occur in Silicon
- Why It Is Called "Physical Unclonable"
- How a PUF Operates
- Differences Between PUFs and Standard Device IDs
- How PUFs Differ from TPMs and Secure Elements
- Why PUFs Are Critical in Physical AI
- Shifting from Human Identity to Machine Identity
- PUF × Hash Chain Integration
- Generic PUF vs. SEES Chip Fingerprint Technology
- Building a Chain of Trust from Silicon to AI Inference and Action
- Industries Set to Benefit from PUF Deployment
- The Imperative of "Machine Zero Trust"
- Summary
- Frequently Asked Questions
What Is a PUF (Physical Unclonable Function)?
A PUF is a hardware security technology that leverages microscopic physical variations inherent in semiconductor manufacturing to generate device-unique responses and cryptographic material.
Even for chips produced using identical fabrication masks and processes, manufacturing two semiconductors with 100% identical physical characteristics is practically impossible. PUF technology exploits these microscopic silicon variations to anchor unique device identification and generate or derive hardware-bound cryptographic keys.
Why Microscopic Physical Variations Occur in Silicon
Semiconductor fabrication requires extreme engineering precision. However, at sub-micron process nodes, unavoidable microscopic variations occur across interconnect wiring, transistor threshold voltages, electrical characteristics, propagation delays, and memory cells.
Crucially, designers do not intentionally manufacture these differences; they are natural physical artifacts of the fabrication process itself.
PUF technology harnesses these unique physical variations as a hardware-bound identity anchor.
Why It Is Called "Physical Unclonable"
Literally translated, a Physical Unclonable Function is a mathematical/physical operation that cannot be physically cloned.
With standard digital device IDs, a value like "Device ID = 123456" is stored in non-volatile memory (NVM). If that memory content is extracted or copied, an adversary can easily flash the exact same ID onto unauthorized hardware.
In contrast, a PUF derives its identity from the unique physical characteristics of the silicon chip itself.
This provides a fundamentally different approach to hardware uniqueness compared to storing digital static keys in memory.
The term "Unclonable" reflects the physical difficulty of replicating microscopic silicon structures. In real-world security, actual resistance to attack depends on the PUF architecture, circuit implementation, evaluation methodology, and the overarching system authentication protocols.
How a PUF Operates
While various PUF architectures exist, one fundamental operational mechanism is the Challenge-Response Protocol.
When an external input (Challenge) is applied to the PUF circuit, the unique physical variations of the silicon evaluate the signal to output a hardware-unique signature (Response).
When the same Challenge is applied to a different chip, the unique physical characteristics of the second chip produce a different Response. This property is directly applied to hardware authentication.
Note that not all PUF architectures rely on a direct challenge-response paradigm. Depending on the design (e.g., SRAM PUF), PUFs are frequently used for key generation, key derivation, and hardware security anchors.
Differences Between PUFs and Standard Device IDs
The fundamental distinction between a standard digital device ID and a PUF lies in where the root anchor of identity resides.
| Comparison Item | Standard Device ID | PUF (Physical Unclonable Function) |
|---|---|---|
| Identity Foundation | Digital values stored in non-volatile memory | Inherent physical silicon variations |
| Uniqueness Anchor | Depends on provisioned static strings | Utilizes unique hardware physical properties |
| Cloning Resistance | Relies entirely on memory readout protection | Leverages physical unclonability of silicon microstructures |
| Cryptographic Keys | Must be written and stored in flash/EEPROM | Can be dynamically derived/generated on-demand |
| Hardware Coupling | Varies by software/firmware implementation | Intrinsically bound to the physical semiconductor substrate |
How PUFs Differ from TPMs and Secure Elements
While PUFs are sometimes confused with TPMs (Trusted Platform Modules) or Secure Elements (SEs), they are distinct security components.
A TPM or Secure Element is a secure hardware coprocessor designed to store cryptographic keys, perform cryptographic acceleration, and enforce secure boot/attestation.
A PUF, by contrast, is a hardware feature/circuit that leverages physical silicon variations to generate or derive device-unique keys and signatures.
They are not mutually exclusive technologies; rather, advanced secure hardware chips often incorporate internal PUF circuits as the root anchor to protect stored keys without placing raw secrets in flash memory.
Why PUFs Are Critical in Physical AI
In Physical AI architectures, sprawling networks of sensors, cameras, robots, and edge nodes continuously feed real-time telemetry into AI inference engines.
For instance, if an unauthorized rogue device impersonates "Sensor A" and transmits false "Temperature Normal" telemetry, the receiving AI model will process that corrupt data as legitimate, leading to unsafe autonomous control commands.
When evaluating the trustworthiness of input data feeding AI models, verifying the data payload alone is insufficient--systems must also answer: "Did this data originate from a verified, authentic physical device?"
Therefore, in Physical AI ecosystems, Device Trust acts as a fundamental pillar supporting Data Trust.
Shifting Focus from Human Identity to Machine Identity
Traditional IT security centered heavily on verifying human users via credentials, passwords, smart cards, and biometrics ("Who is accessing the system?").
In autonomous Physical AI environments, security must expand to encompass Machine Identity--verifying "Which machine or device generated this signal?"
PUF × Hash Chain Integration: Bridging Device Trust and Data Integrity
Device Trust alone cannot protect a Physical AI ecosystem. Even if data originates from an authentic device, if the telemetry payload is tampered with in transit or during local storage, system integrity fails.
This necessitates an integrated approach combining Device Authenticity and Data Integrity.
By leveraging PUF-based technology to authenticate hardware devices, systems establish a verified Machine Identity. Concurrently, technologies like Hash Chains verify that data payloads remain completely untampered post-generation.
Uniting Device Trust with Data Integrity builds an unbroken Chain of Trust spanning from physical device origins directly to AI inference engines.
Generic PUF Technology vs. SEES "Chip Fingerprint" Technology
Generic PUF refers to hardware security primitives that exploit silicon micro-variations to generate hardware-unique signatures, keys, or authentication responses.
A wide variety of PUF circuit designs exist (e.g., SRAM PUF, Arbiter PUF, Ring Oscillator PUF), serving diverse purposes like device attestation and cryptographic key storage replacement.
By contrast, SEES Inc. is researching and developing proprietary "Chip Fingerprint" technology specifically tailored to anchor device identification from physical semiconductor variations for Physical AI architectures.
While generic PUFs act as isolated hardware security primitives, SEES utilizes Chip Fingerprints as the root anchor for Device Trust within an integrated architecture. Combined with Hash Chains and Scramble Memory, this establishes a comprehensive Physical AI Trust Infrastructure spanning devices, data payloads, network transmission, and physical actuators.
Comparing Generic PUF with the SEES Approach
| Comparison Item | Generic PUF Primitives | SEES Integrated Approach |
|---|---|---|
| Technical Anchor | Physical variations in semiconductor substrates | Chip Fingerprint technology leveraging silicon physical variations |
| Primary Scope | Device authentication, cryptographic key storage replacement | Serves as the hardware root of trust for Machine Identity |
| Device Identification | Applied per component requirements | Integrated into Machine Identity for Physical AI networks |
| Data Tamper Verification | Not a primary feature of standalone PUFs | Integrates directly with software Hash Chains |
| Data at Rest Protection | Not a primary feature of standalone PUFs | Integrates directly with Scramble Memory |
| Physical AI Integration | Component-level hardware security option | Foundation layer for Physical AI Trust Infrastructure |
| Scope of Trust Chain | Provides hardware-level uniqueness primitives | Extends unbroken trust: Chip → Device → Data → AI → Action |
Why Chip Identification Alone Cannot Fully Protect Physical AI
In Physical AI ecosystems, verifying that a transmitting chip is authentic does not automatically guarantee that the streaming data reaching the AI is completely trustworthy.
Even if data is generated by a legitimate chip, if that payload is intercepted, modified, or replayed during transmission or local storage, the AI model will receive corrupted inputs.
Therefore, SEES uses Chip Fingerprints to establish Device Trust at the chip layer, while integrating Hash Chains for data payload integrity/continuity and Scramble Memory for local storage protection, realizing a holistic Physical AI Trust Infrastructure.
Building a Chain of Trust from Silicon to AI Inference and Action
Establishing security for Physical AI requires looking beyond the AI model itself to secure the unbroken pipeline from data-generating silicon to physical mechanical execution.
In this framework, silicon-level identity authenticates the host device. Next, cryptographic mechanisms verify that streaming telemetry generated by the device remains unaltered in transit, enabling the AI engine to execute inference based strictly on verifiable data.
Because AI inferences directly translate into physical motion across robotics, commercial drones, and automated manufacturing, SEES treats Chip → Device → Data → AI → Action as an indivisible Chain of Trust.
Industries Set to Benefit from PUF Deployment
Technologies that leverage physical hardware-bound uniqueness are essential across all sectors managing large-scale deployments of autonomous edge devices.
Authenticating robotic controllers, articulated arms, and field sensor payloads.
Providing unique hardware attestation for flight controllers and telemetry hardware.
Anchoring Machine Identity across connected ECUs and ADAS sensor modules.
Securing field sensors, PLCs, industrial gateways, and edge compute nodes.
Enabling chip-level unique identification and hardware key derivation without flash storage.
Managing Machine Identity across massive scale-out deployments of IoT nodes.
Verifying hardware authenticity and provenance from fabrication to field operation.
Building foundational Device Trust for hardware feeding telemetry into AI models.
The Imperative of "Machine Zero Trust" in the Physical AI Era
Zero Trust architectures discard implicit trust based on network perimeters, requiring continuous authentication for every session.
In Physical AI, this continuous verification mandate must extend beyond human users to physical machines and edge devices.
A device is not authentic simply because it connects to a local network. An endpoint is not trustworthy merely because it presents an IP address. A node is not verified simply because it transmits a digital static ID string.
In Physical AI, establishing robust physical Machine Identity and linking it to data and AI trustworthiness represents a critical security challenge.
Summary | Verifying "Is This Hardware Device Authentic?"
PUF is a hardware security technology that utilizes physical silicon variations introduced during semiconductor manufacturing.
In Physical AI, vast ecosystems of edge machinery--including sensors, industrial robots, drones, and actuators--communicate continuously with AI decision engines.
Consequently, security must determine not just "which user is logged in," but "which specific physical machine generated this data payload?"
SEES Inc. utilizes Chip Fingerprints derived from physical silicon variations as the root anchor for Device Trust, pairing it with Hash Chains and Scramble Memory to construct a robust Physical AI Trust Infrastructure.
Frequently Asked Questions About PUF
What is a PUF (Physical Unclonable Function)?
A PUF is a hardware security technology that utilizes microscopic physical variations introduced during semiconductor manufacturing to generate device-unique signatures, keys, or responses.
Is a PUF literally a "semiconductor fingerprint"?
"Semiconductor fingerprint" is an intuitive metaphor. In technical reality, physical properties and implementation mechanisms vary depending on the specific PUF architecture (e.g., SRAM PUF, Ring Oscillator PUF).
Are PUFs 100% impossible to clone under any condition?
The term "Unclonable" describes the extreme physical difficulty of replicating sub-micron silicon variations. Overall security relies on the complete system design, including PUF stability, enrollment protocols, and authentication layers.
How do PUFs differ from standard digital device IDs?
Standard device IDs rely on digital strings stored in non-volatile memory that can potentially be extracted. PUFs derive identity directly from the physical silicon structure of the device itself.
Is a PUF the same as a TPM or Secure Element?
No. A TPM or Secure Element is a secure hardware coprocessor providing cryptographic storage and processing. A PUF is a technology that leverages silicon physical variations for hardware uniqueness, and both are often combined within secure systems.
How do generic PUFs differ from SEES Chip Fingerprint technology?
Generic PUFs provide component-level hardware uniqueness primitives. SEES Chip Fingerprints act as the foundational anchor within an integrated Trust Infrastructure, combining Hash Chains and Scramble Memory to extend unbroken trust from silicon to data, AI inference, and real-world physical action.
Why are PUFs critical for Physical AI?
Physical AI relies on streaming telemetry from vast networks of sensors and edge nodes to execute real-world actions. Establishing hardware Device Trust via PUFs ensures that AI models only process data feeds originating from authentic physical machines.
Can a PUF alone secure a Physical AI ecosystem?
No. A PUF provides hardware-level device authentication. Comprehensive Physical AI security requires combining Device Trust with data payload integrity verification, network transmission security, access control, and AI model protection.
SEES Inc. conducts R&D on core data security technologies--including Chip Fingerprints, Hash Chains, and Scramble Memory--to build Trust Infrastructure for the Physical AI era. Contact us for technical evaluation, joint development, or PoC opportunities.
Contact SEES